Building the trust layer beneath every digital transaction — identity, access, data, and emerging technology, secured end-to-end.
Digital Trust Solutions from HawkTech Advance Solutions help enterprises verify every user, device, and transaction before granting access — combining Zero Trust architecture, Identity & Access Management (IDAM), data security controls, and emerging-technology safeguards into one managed framework. As a Managed Security Service Provider (MSSP) based in Delhi NCR, we help businesses reduce breach risk, meet compliance mandates, and scale securely without slowing down operations.
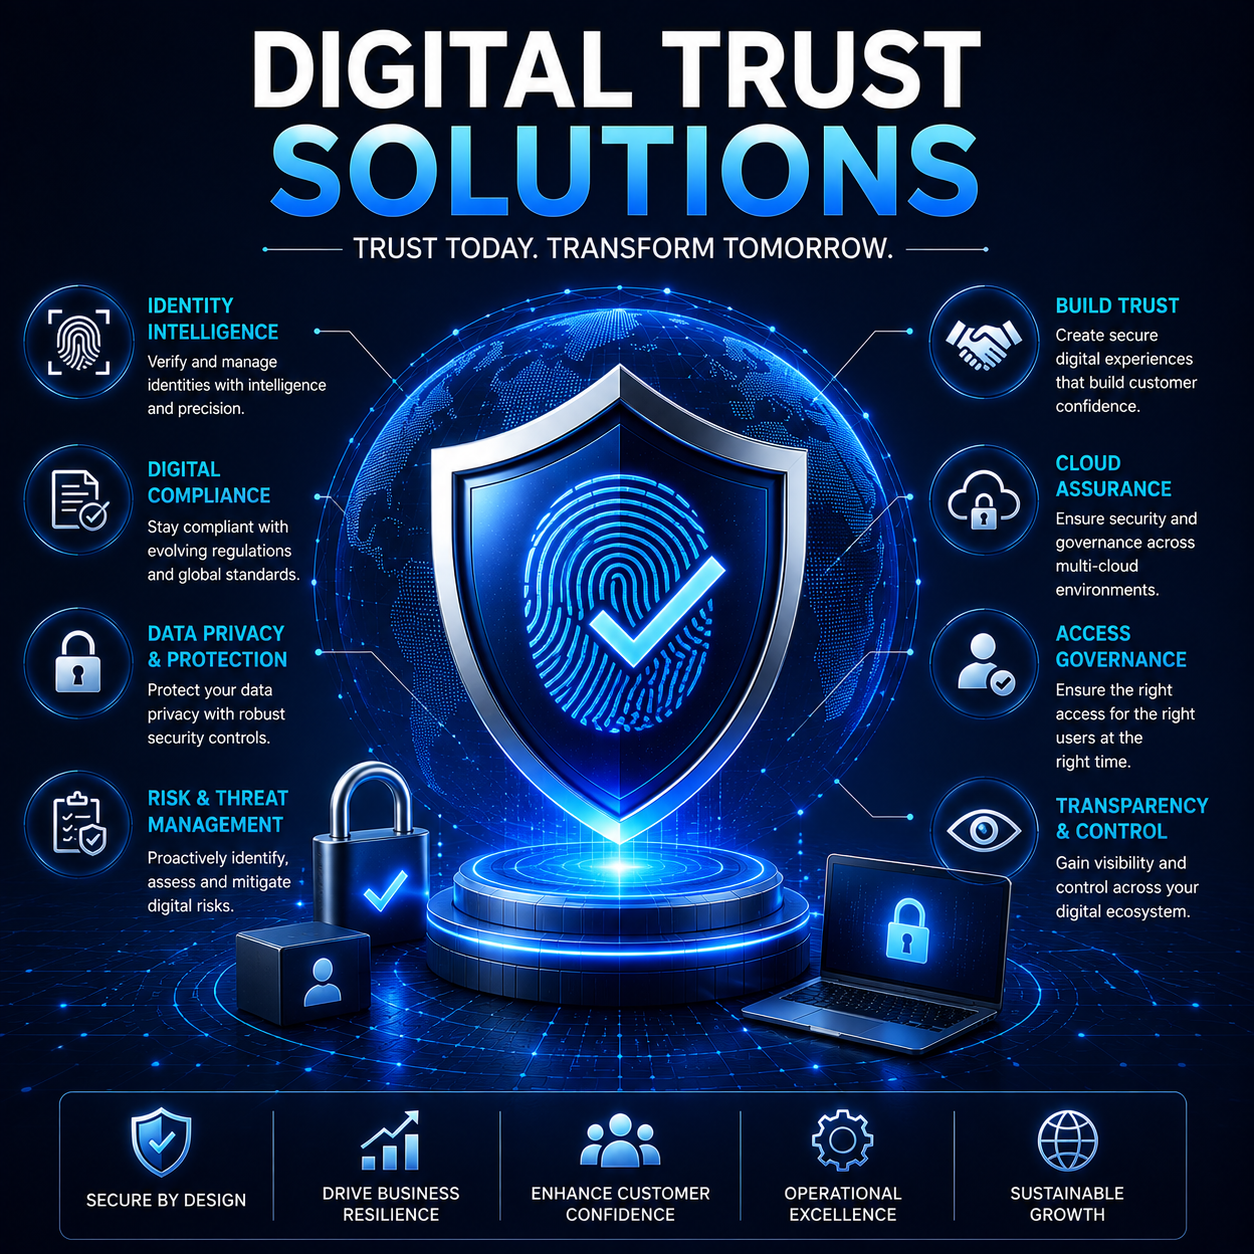
Trust isn't a checkbox — it's continuously verified. Every identity, device, and data flow is authenticated, monitored, and re-validated, never assumed. That's the principle Zero Trust and IDAM are built on, and it's the principle behind everything we deliver.
Emerging technology security protects AI systems, IoT devices, cloud-native applications, and automation pipelines from risks that traditional security tools weren’t built to catch. HawkTech assesses and secures new technology adoption from day one, so innovation never outpaces protection.
New technology creates new attack surface faster than most security teams can map it. AI models, IoT/OT devices, APIs, and cloud-native workloads all introduce risks — data leakage, model manipulation, unmanaged device access, insecure integrations — that legacy tools weren’t designed to detect. HawkTech evaluates emerging technology deployments before and during rollout, building security controls into the architecture rather than bolting them on afterward.
Zero Trust is a security model built on “never trust, always verify” — no user, device, or application is trusted by default, even inside the network perimeter. HawkTech designs and implements Zero Trust architecture that continuously authenticates every access request across your environment.
Perimeter-based security assumes that anything inside the network is safe — an assumption that no longer holds with remote work, cloud adoption, and third-party access. Zero Trust replaces that assumption with continuous verification: every user, device, and application must prove identity and posture before every access request, every time. HawkTech implements Zero Trust in phases — starting with identity and network segmentation, then extending to applications and data — so you get measurable risk reduction without disrupting operations.
Data security and protection safeguards sensitive business and customer data across its lifecycle — at rest, in transit, and in use — through encryption, masking, access controls, and loss-prevention monitoring. HawkTech’s data security services help enterprises stay compliant while reducing exposure to breaches and leaks.
Data is the asset attackers want most, and the one regulators scrutinize hardest. HawkTech’s data security services cover the full lifecycle: classifying sensitive data, encrypting it at rest and in transit, masking it in non-production environments, and monitoring for unauthorized movement or exfiltration in real time. The result is a data environment that’s usable for the business and defensible for compliance — whether that’s DPDP Act, GDPR, or industry-specific mandates.
IDAM (Identity and Access Management) governs who can access what, when, and how, across every system in your organization. HawkTech’s IDAM solutions combine single sign-on, multi-factor authentication, and lifecycle governance to eliminate unmanaged access — a leading cause of breaches.
Most breaches trace back to identity — a stolen credential, an orphaned account, an over-permissioned user nobody reviewed. HawkTech’s IDAM solutions bring every identity, human and non-human, under a single governance framework: provisioning access on day one, adjusting it as roles change, and revoking it immediately on exit. Combined with MFA and SSO, this closes the identity gaps that attackers rely on most.
A Digital Trust Solution is a combined framework of identity management, Zero Trust security, and data protection controls that verifies every user, device, and transaction before granting access — reducing breach risk across an organization's digital environment.
IDAM (Identity and Access Management) governs who has access to what. Zero Trust is the broader security model that continuously verifies that access at every request, regardless of network location. IDAM is a core building block of a Zero Trust architecture.
Any business handling sensitive customer, financial, or operational data benefits from Zero Trust and IDAM — attackers target smaller businesses precisely because access controls are often weaker. HawkTech scales implementation to business size and budget.
Timelines vary by scope, but HawkTech typically phases implementation — starting with identity and access foundations (4–6 weeks), followed by Zero Trust network segmentation and data protection controls layered in over subsequent phases.
Yes. Our data security and IDAM controls are designed to align with the DPDP Act and relevant industry compliance frameworks, with audit-ready reporting built in.

Take the First Step Toward Cyber Resilience
Tower C, Iconic Corenthum,Noida Uttar Pradesh,201310, India
Copyright © 2026 HawkTech Advance Solutions. Powered by Hawktech Digital Solutions
We use cookies to improve your experience on our site. By using our site, you consent to cookies.
Manage your cookie preferences below:
Essential cookies enable basic functions and are necessary for the proper function of the website.